Supermarket Refrigeration Controllers Hit Across Europe in November 2026
- Published
- Author
- Dennis Knake
- Reads
- 403
Remote defrost changes disrupted food retailers in at least six countries, renewing concerns about internet exposed refrigeration controllers and default passwords.
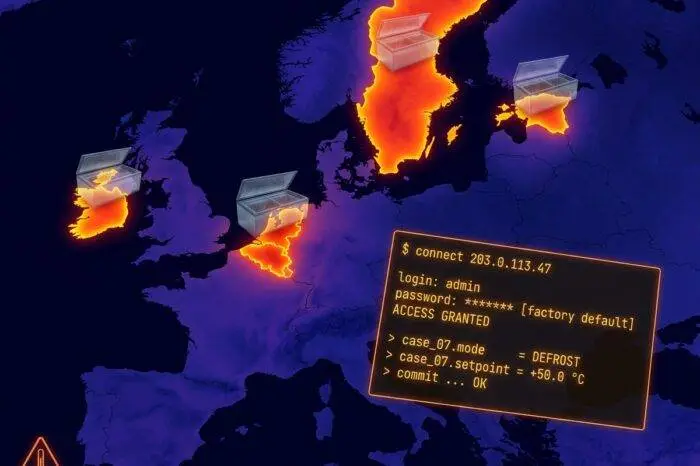
Remote access to refrigeration controls turned into a direct cold chain risk overnight into November 2, 2026. Unknown attackers switched supermarket evaporators into defrost mode across Europe, causing freezer temperatures to rise and disrupting stores and smaller food businesses. The incidents affected controllers from Danfoss and, in Belgium, Copeland. A similar attack in France had taken place about three weeks earlier.

Defrost mode became the point of failure
Evaporators periodically enter defrost mode to melt accumulated ice. In the reported incidents, attackers triggered that operating mode remotely, heating refrigerated cabinets instead of keeping products cold. Belgian freezers reached about 15 degrees Celsius, according to broadcaster RTBF. Retailers in Sweden reported setpoints as high as 50 degrees Celsius.
The disruptions crossed several retail groups and business types. In Belgium, more than 70 sites were affected. Delhaize reported at least 40 stores, Carrefour 15, Intermarché up to 15, and Spar five, according to figures compiled by VRT NWS. The affected locations included smaller Delhaize formats, such as Shop & Go outlets at Q8 fuel stations, as well as an IKEA store in Mons and several butcher shops.
Retailers in Sweden, including ICA and Coop, also reported affected stores. In Ireland, SuperValu reported disruptions at 13 of its 223 stores. Danfoss said at least 17 smaller businesses in the Netherlands were attacked, mostly butcher shops. Incidents were also reported in Luxembourg and Estonia.
German cases emerged on November 3. A CAP store in Wuppertal said an external intervention had heated its refrigeration equipment and that all affected goods had to be discarded. Edeka Ernst in Reisbach, Lower Bavaria, reported temperatures of up to 50 degrees Celsius. In Raesfeld, North Rhine-Westphalia, a Rewe operator found cabinets in defrost mode, also reaching up to 50 degrees. That store used a Danfoss controller. A connection between the German cases and the wider European incidents has not been confirmed; details came from the operators.
Exposed controllers and default credentials
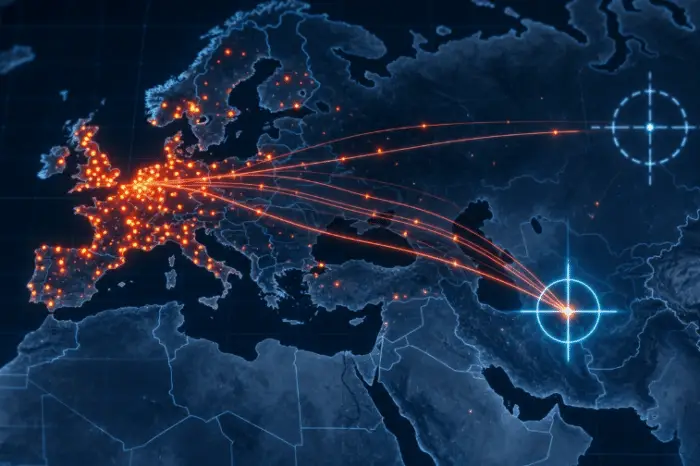
The mechanism resembles the October attack on French supermarket refrigeration, which the Paris prosecutor’s office said affected around 700 victims. Danfoss controllers were involved again, while Belgian contractor Sabcobel described the same method of manipulating refrigeration systems. Copeland equipment was also affected in Belgium. Authorities have not identified the specific vulnerability used.
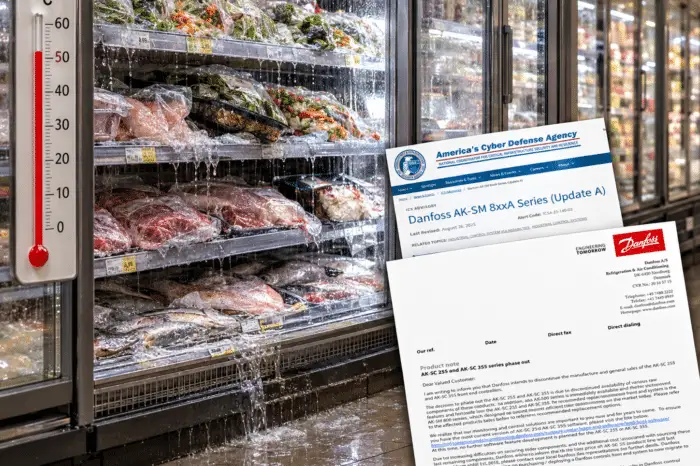
Danfoss told Dutch broadcaster NOS that systems attacked in the Netherlands were accessible online without a secured network and used a default password. After the French incident, Danfoss had asked customers on October 13 to disconnect their systems from the internet. Most reportedly did so, but some equipment remained exposed.
That points to a practical weakness in remote industrial equipment: a controller reachable from the public internet can be operated from outside the business if its access controls are inadequate. Security firm Spotit’s Keanu Nys told VRT that refrigeration systems have no reason to be openly accessible. Remote maintenance can instead use a VPN, which provides an encrypted connection into an internal network.
Older equipment complicates remediation. Danfoss AK-SM 800 controllers, for example, have not received security updates for years. Sabcobel CEO Stephan Moelans said that a software update alone is insufficient for some systems and that a physical modification is needed. About twenty of the hundreds of systems Sabcobel manages in Belgium were affected.
Attribution remains unresolved
No group has claimed responsibility, and there was no ransom demand. It is also unknown whether the November attackers were the same people behind the October incident. Security researcher Sijmen Ruwhof told NOS that the spread across multiple retail chains suggests the operation was not aimed at one particular company.
Belgium’s Centre for Cybersecurity has left open whether the activity came from criminals, state backed actors or hacktivists. Danfoss has said controllers of this type were targeted in supermarkets in Russia and Israel in 2022, but that history does not identify who was responsible for the current incidents. Belgium’s federal prosecutor’s office opened an investigation.
What operators should check
Supermarkets, franchisees, butcher shops and refrigeration contractors all depend on controls that may be maintained remotely. The immediate technical priorities are to remove direct public internet access, replace default passwords and route remote maintenance through a secured connection such as a VPN. Operators also need to identify equipment that no longer receives security updates and assess whether it requires modification or replacement.
The incidents show how a control function intended for routine equipment maintenance can affect product temperatures across multiple sites. After the French attack, manufacturers, contractors and cybersecurity organizations had already urged operators to secure exposed systems. The November disruptions suggest that the remaining work is practical and site specific: inventory the controllers, verify how they can be reached, and confirm that remote access is protected.


